Management Use Cases
Overview
Android Enterprise supports four management use cases. The use case is chosen at enrollment and determines how much of the device the MDM controls. The use cases are defined by Google and are the same in every MDM, but each MDM uses its own names for them. For more information, see Google's Android Enterprise overview.
Most Datalogic customers enroll their devices as dedicated devices, because no employee Google account needs to be linked to the device. Instead, the MDM creates a managed Google account for the device automatically. The use case is set in the enrollment profile you create in your MDM, as covered in Enrollment.
Comparison
| Fully managed (dedicated devices) | Fully managed (work-only) | Work profile (company-owned) | Work profile (BYOD) | |
|---|---|---|---|---|
| Device ownership | Company | Company | Company | Employee |
| MDM control | Entire device | Entire device | Work profile, plus device-wide policies | Work profile only |
| Personal use | No | No | Yes, in the personal profile | Yes, in the personal profile |
| Assigned user | No, shared or unattended | Yes | Yes | Yes |
| User sign-in | None (account created automatically) | Work account | Work account | Work account |
| Typical use | Warehouse, retail, kiosk, and signage devices | One employee's work device (Teams, Outlook) | Company devices also used personally | Employees' personal phones |
Names in each MDM
Dedicated devices are a subset of fully managed devices that serve a specific purpose, so most MDMs use the same enrollment type for both. Microsoft Intune has a separate enrollment profile for each.
| Fully managed (dedicated devices) | Fully managed (work-only) | Work profile (company-owned) | Work profile (BYOD) | |
|---|---|---|---|---|
| SOTI MobiControl | Work Managed | Work Managed | Work Profile on Company-Owned Device | Work Profile |
| Microsoft Intune | Corporate-owned dedicated devices | Corporate-owned, fully managed user devices | Corporate-owned devices with work profile | Personally-owned devices with work profile |
| SureMDM | Fully Managed Devices (Device Owner) | Fully Managed Devices (Device Owner) | Work Profile on Company Owned (WPCO) | Profile Owner |
| Workspace ONE | Work Managed | Work Managed | Corporate-Owned, Personally Enabled (COPE) | Work Profile |
Full management for dedicated devices (recommended)
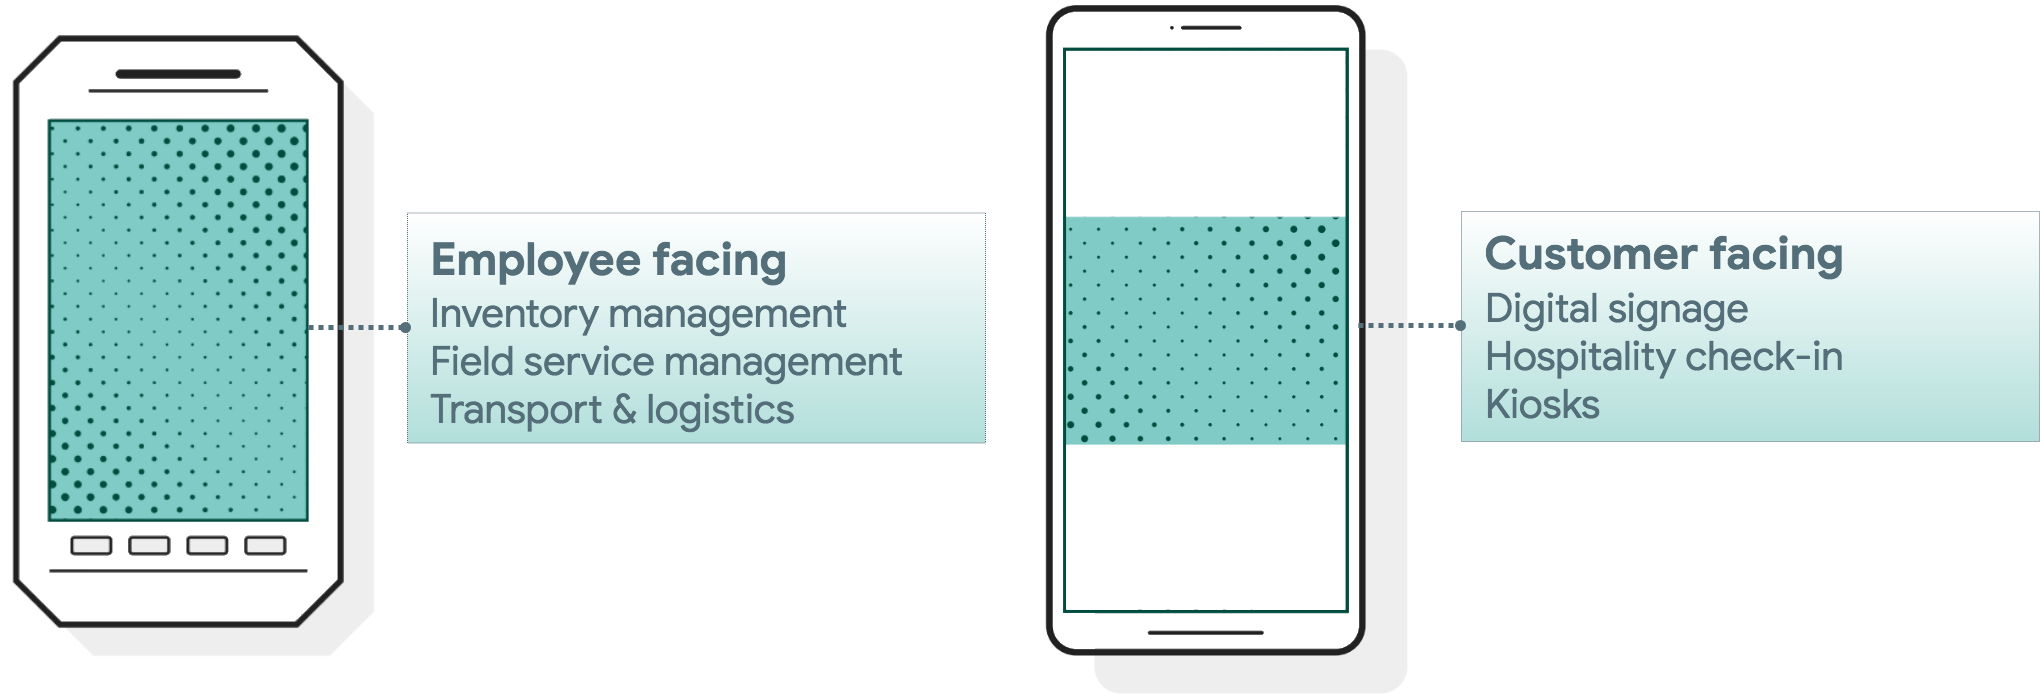
Dedicated devices (formerly called corporate-owned single-use, or COSU) are fully managed devices that serve a specific purpose, such as employee-facing warehouse and industrial devices or customer-facing kiosks and signage. They are not assigned to a specific user and are typically locked to a single app or set of apps. No one signs in with a Google or work account during enrollment; a managed Google Play account is created for the device automatically. As with any fully managed device, the MDM can apply Android's full range of management policies, including control of the lock screen, status bar, keyboard, and other features to keep users from opening other apps or changing the device.
Full management for work-only company-owned devices
A fully managed work-only device is company-owned, used only for work, and assigned to one employee. The MDM agent is the device owner and can apply Android's full range of management policies, including device-level policies that are not available with a work profile. Unlike a dedicated device, the user signs in with their work account during enrollment, which is required for apps that depend on the user's identity, such as Microsoft Teams and Outlook. This use case is rarely used on Datalogic devices.

Work profile for mixed-use company-owned devices
A work profile can also be used on a company-owned device that the employee is allowed to use personally. The organization fully manages the work profile. Because the device is company-owned, the organization can also apply device-wide policies, such as Wi-Fi settings or blocking USB file transfers, and some restrictions on the personal profile, such as blocking certain apps. The personal profile's apps, data, and usage remain private.

Work profile for employee-owned devices
Employee-owned devices are also known as Bring Your Own Device (BYOD). A work profile is a separate, self-contained space on the device for work apps and data. The employee keeps using their device as normal, with personal apps and data in the personal profile. The organization fully manages the apps, data, and settings in the work profile, but cannot see or access the personal profile.
